Aviation cyber resilience remains a European policy concern a year after ransomware disrupted passenger-processing systems at several major airports. EASA scheduled a dedicated hybrid event on the cybersecurity threat landscape for 12 October 2026, bringing a current institutional focus to the September 2025 airport outage.
The EASA event notice identifies growing dependence on information technology across aviation and the potential for cyberattacks to disrupt operations. Its agenda was updated on 30 September.
The notice is evidence of the planned discussion, not a published record of its conclusions. It does not announce that a particular vulnerability has been eliminated or that airlines and airports have adopted a new common standard.
The earlier outage affected passenger processing
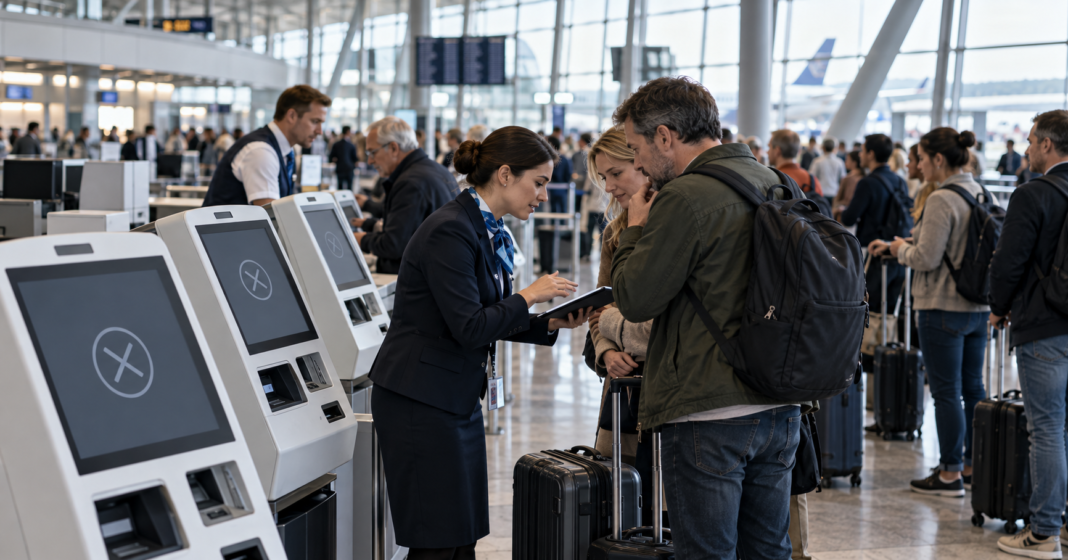
The BBC report of 22 September 2025 described an attack affecting Collins Aerospace software used for check-in and boarding. ENISA identified ransomware, while airports used manual procedures and alternative systems as recovery continued.
That incident should retain its original date. It is not evidence of a fresh attack in October 2026, nor does a check-in outage by itself establish a compromise of aircraft flight systems.
Operational resilience needs a precise scope
The distinction between passenger services and flight safety is essential. Shared suppliers can connect several airports operationally, so disruption can spread beyond a single terminal even when the affected function remains limited.
EASA’s current focus provides a basis for discussing that dependency. A claim that recovery is complete, that a new attack has occurred or that a particular safeguard has failed would require additional evidence beyond an event listing and the historical BBC account.